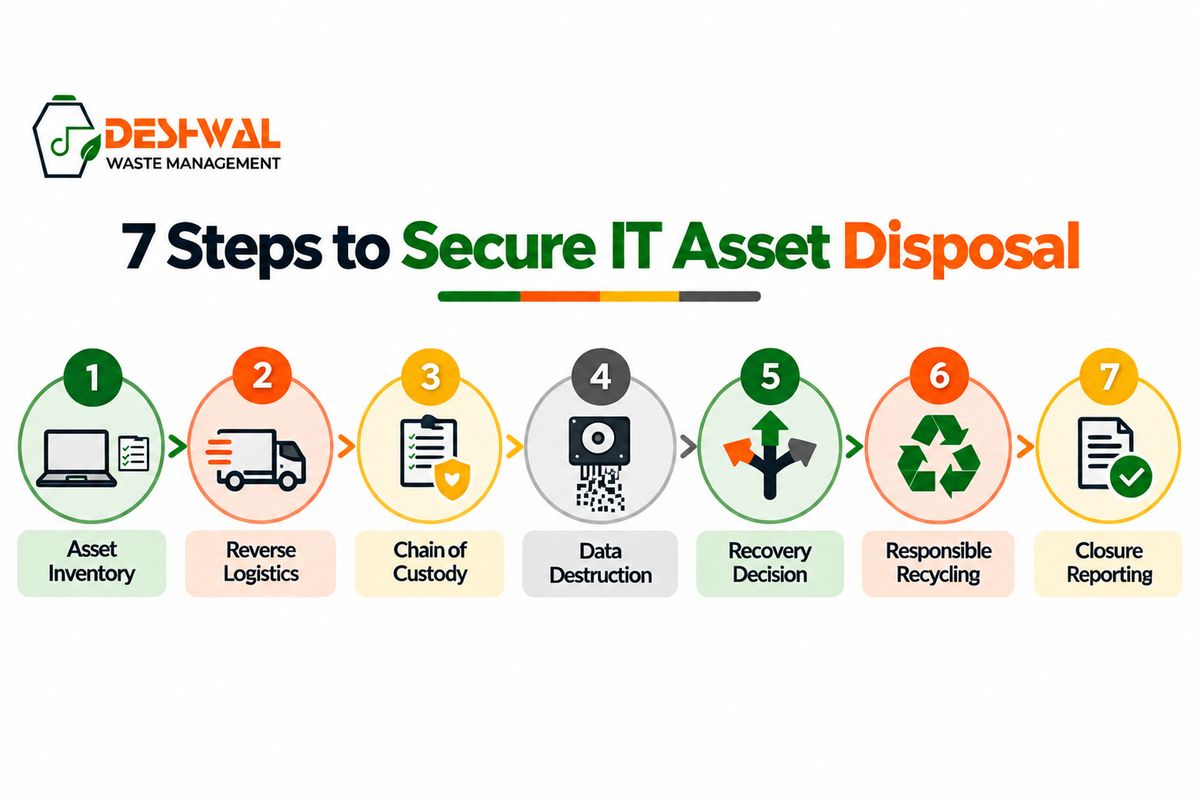
Secure IT asset disposal means retiring enterprise IT assets through inventory, reverse logistics, chain of custody, data sanitisation or destruction, asset recovery, recycling and closure reporting. For Indian enterprises, the process should protect data, recover value where possible, handle e-waste responsibly and create records that can be reviewed later.
Why secure IT asset disposal matters for Indian enterprises
For many enterprises, IT asset disposal begins when old hardware has to be cleared from the office.
Laptops are replaced. Desktops are removed. Servers are decommissioned. Storage drives, monitors, printers, networking devices, UPS systems, cables, batteries and accessories are bundled into a disposal lot. Procurement asks for quotes, and the fastest pickup or highest recovery value often becomes the preferred option.
That approach can create risk.
Retired IT assets are not ordinary scrap. They may still contain business data, employee records, customer information, credentials, financial documents, source code or sensitive configuration files. They may also contain recoverable components, lithium-ion batteries, lead-acid battery waste, PCBs, metals and plastic fractions recovered from e-waste.
For Indian enterprises, secure disposal should answer more than one question.
It should not only ask:
“Who will remove these assets?”
The better question is:
“Can we prove how every asset was collected, tracked, sanitised, recovered, recycled or closed?”
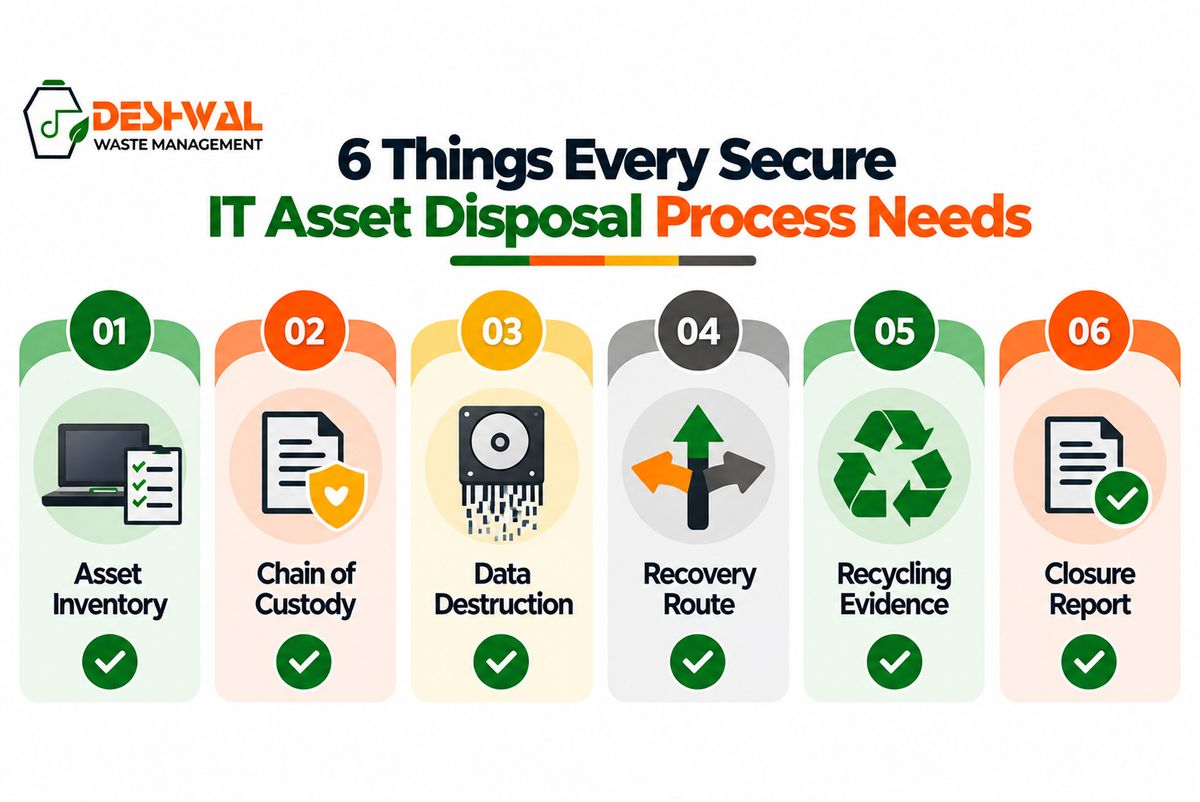
That is where secure IT asset disposal becomes a structured process. It protects data, reduces uncertainty, supports recovery value and creates evidence for IT, procurement, security, finance, ESG and compliance teams.
What secure IT asset disposal means
Secure IT asset disposal is the controlled retirement of IT assets after they are no longer needed in active use.
It includes identifying assets, collecting them through planned reverse logistics, maintaining chain of custody, addressing data risk, recovering value where possible, recycling responsibly and maintaining closure records.
In enterprise environments, this process may include laptops, desktops, servers, hard drives, SSDs, storage systems, networking devices, monitors, printers, UPS systems, batteries, cables, access devices and other IT infrastructure assets.
Secure disposal also becomes important during office closures, IT refreshes, branch exits, server room clean-ups and data-centre decommissioning projects. In these cases, the disposal process may involve both loose IT assets and fixed infrastructure such as racks, UPS units, networking equipment, storage systems, cabling and related hardware.
A secure process does not treat everything as a mixed scrap lot.
It asks what each asset is, where it came from, whether it contains data, whether it has recovery value, whether it needs recycling and what proof is required after closure.
Build a clear asset inventory
Secure disposal begins before pickup.
The first step is to create a clear inventory of assets being retired. This inventory should include asset category, asset tag, serial number, location, user or department, condition, quantity and data-bearing status.
For example, an enterprise disposal lot may include laptops, desktops, servers, monitors, printers, hard drives, SSDs, networking devices, UPS systems, lithium-ion batteries, lead-acid battery waste, cables and accessories.
The inventory matters because the process becomes weak when the asset list is weak.
If the enterprise does not know what should be collected, it cannot prove what was collected. If it cannot prove what was collected, it cannot prove what was sanitised, recovered, recycled or closed.
A strong inventory also helps procurement and finance teams reconcile recovery value with actual assets instead of relying only on a batch-level quote.
Plan reverse logistics before pickup
Reverse logistics is the movement of retired assets from enterprise locations back into a controlled processing route.
For a single office, this may be simple. For a multi-location enterprise, it may involve branches, plants, warehouses, IT stores, data centres, remote users or regional offices.
Collection planning should define pickup locations, site contacts, asset quantities, packaging needs, collection dates, documentation requirements and exception handling.
This matters because secure IT asset disposal is not just a transport activity.
A retired laptop may still contain data. A server may contain storage media. A UPS system may include battery waste. A network device may contain configuration data. A branded device may create reputation risk if it moves through unclear channels.
Where office closures, branch exits, lab shutdowns or IT refreshes are involved, enterprises may also need office and IT-infrastructure dismantling support. This helps separate IT assets, data-bearing equipment, battery waste and recyclable streams from general office removal activity.
Maintain chain of custody
A pickup receipt is useful, but it is not the same as chain of custody.
Chain of custody records who handled the assets, where they moved, when they were received and what happened next. It helps enterprises reduce uncertainty after assets leave their premises.
A mature custody trail may include pickup acknowledgement, asset or batch details, serial-number references where applicable, transfer records, receiving confirmation, mismatch notes, damaged-asset notes and movement into data destruction, grading, recovery, recycling or final disposition.
Receiving and reconciliation are important at this stage.
When assets arrive at the receiving point, they should be checked against the collection record. The team should identify missing assets, extra assets, damaged devices, missing drives, mismatched serial numbers or category differences.
These exceptions should not disappear inside a batch summary.
They should be recorded, routed and closed.
Identify data-bearing assets
Not every IT asset carries the same level of data risk.
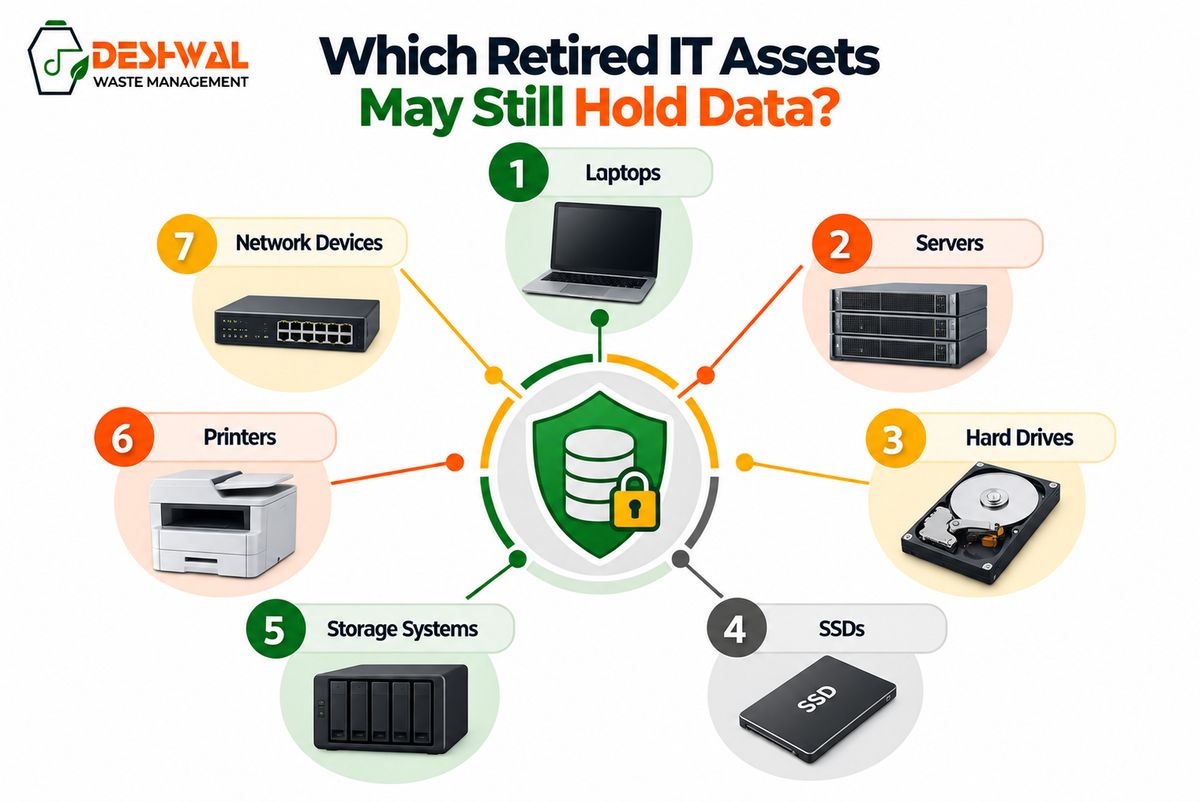
A keyboard and a hard drive do not need the same handling. A monitor and a server do not carry the same exposure. A printer, laptop, desktop, SSD, backup device or network appliance may store information or configuration data.
That is why data-bearing assets should be identified before reuse, resale, refurbishment, recycling or disposal.
This may include laptops, desktops, servers, hard drives, SSDs, storage arrays, backup devices, mobile devices, printers with storage components and networking equipment with memory or configuration data.
This stage is where secure IT asset disposal overlaps with ITAD. A strong IT asset disposal process should not only remove assets. It should also create evidence around asset movement, data handling, route decisions and final closure.
Complete data sanitisation or physical data destruction
Data destruction is one of the most important parts of secure IT asset disposal.
Deleting files is not enough. Formatting a system is not enough. Resetting an operating system is not enough.
For data-bearing assets, enterprises need a process that shows how the data was sanitised, destroyed or rendered unrecoverable before the asset moves into reuse, resale, refurbishment, recycling or disposal.
Depending on asset type, media condition, data sensitivity and enterprise policy, data handling may include software-based wiping, purge methods, degaussing, drilling, shredding or physical destruction.
A useful data-destruction record should show which asset was processed, what method was used, whether the process passed or failed, how failed or non-wipeable media was handled and what evidence was issued.
The key point is simple: recovery value should never move ahead of data-risk closure.
Decide the right recovery, reuse or recycling route
Not every retired IT asset should go directly into recycling.
Some devices may still have useful life. Some may be suitable for repair, refurbishment, redeployment, remarketing or parts recovery. Some may have no safe or commercial reuse route and should move into recycling or destruction.
This route decision should happen after data risk has been addressed.
The decision may consider working condition, age, specifications, cosmetic condition, component health, battery condition, resale potential, repair viability, data status and enterprise policy.
This is where secure disposal protects both value and control.
A basic disposal process may treat everything as scrap. A stronger process evaluates whether recovery, recycle and reuse, refurbishment coordination, material recovery or destruction is the right route.
Where repair, refurbishment or second-life activity is part of the project, OXYPC and Renew Circuits should be positioned as supporting repair, refurbishment and second-life channels. The main secure disposal, ITAD, recycling and reporting context should remain with Deshwal.
Handle batteries, PCBs, metals and plastic fractions carefully
Secure IT asset disposal also needs proper material handling.
A disposal lot may include lithium-ion batteries from laptops and devices, lead-acid battery waste from UPS systems, PCBs, cables, screens, storage media, metals and plastic fractions recovered from e-waste.
The wording around plastic should stay specific. Enterprises should refer only to plastic fractions recovered from e-waste, not general plastic waste or PET processing.
Battery waste also needs separate attention. Lithium-ion and lead-acid battery waste should be identified and routed through documented handling pathways where relevant.
For battery-related streams, enterprises should consider proper battery recycling routes. For electronics metals, precious metal recovery from electronics may also be relevant within the wider material-recovery process.
The goal is not only to remove material.
The goal is to make the recycling and recovery route clear enough to support later review.
Keep EPR, BRSR and closure records organised
The final stage of secure IT asset disposal is documentation.
A complete closure file may include asset inventory, pickup records, custody records, receiving and reconciliation reports, data sanitisation or destruction evidence, failed-wipe notes, grading decisions, recovery summaries, recycling records, battery-waste records, EPR-support records where applicable and final closure reporting.
For relevant producer or regulated contexts, IT asset disposal and e-waste records may support EPR-related documentation and e-waste annual return filing.
For relevant listed entities, these records may also support BRSR-related inputs. BRSR should not be described as applicable to every enterprise.
A certificate is useful, but it should not carry the full burden of proof.
Secure IT asset disposal should end with a record that can be retrieved, reviewed and defended.
Where Deshwal fits in secure IT asset disposal
Deshwal’s role in secure IT asset disposal is strongest on the return side of the asset lifecycle.
This includes reverse logistics, ITAD, data sanitisation, data destruction, buyback, asset recovery, refurbishment coordination, e-waste recycling and disposal services, lithium-ion and lead-acid battery waste handling, plastic fractions recovered from e-waste, EPR support and compliance reporting.
For enterprises, this matters because IT asset disposal is not a one-department task.
IT needs asset visibility.
Security needs data-risk closure.
Procurement needs accountable execution.
Finance needs recovery-value reconciliation.
ESG and compliance teams need records that can support internal review, EPR-related documentation, BRSR inputs for relevant listed entities and closure reporting.
The goal is not only to clear old hardware.
The goal is to close the asset record with evidence.
To discuss secure IT asset disposal, ITAD and documentation-led closure, contact Deshwal.
FAQs
What is secure IT asset disposal?
Secure IT asset disposal is the controlled process of retiring IT assets through inventory, reverse logistics, chain of custody, data sanitisation or destruction, asset recovery, recycling and closure reporting.
Why is secure IT asset disposal important in India?
It is important because retired IT assets may contain sensitive data, recoverable value, battery waste, recyclable materials and documentation requirements. Enterprises need a controlled process to reduce data-risk gaps and maintain closure evidence.
Is secure IT asset disposal the same as ITAD?
Secure IT asset disposal is closely linked to ITAD. ITAD, or IT Asset Disposition, is the broader process of retiring IT assets through tracking, data destruction, recovery, refurbishment coordination, recycling and reporting.
What assets need secure disposal?
Assets such as laptops, desktops, servers, hard drives, SSDs, storage systems, networking devices, printers, UPS systems, mobile devices and data-centre hardware may need secure disposal, especially if they contain data or recoverable components.
What documents should enterprises maintain?
Enterprises may need asset inventory, pickup records, chain-of-custody documents, receiving records, data sanitisation or destruction evidence, recovery summaries, recycling records, battery-waste records and final closure reports.